
 Join our Discord
Header injection support on BrowserStack Automate
Pass HTTP headers as capabilities in your test sessions with BrowserStack Automate.
Support for HTTP Headers is available only on the Automate Desktop & Mobile Pro Plan. Reach out to the BrowserStack Support team to try this feature. For more details, see the BrowserStack pricing page.
Use HTTP headers to pass additional context to your test session. BrowserStack supports both default HTTP headers along with custom headers that your organization might use.
In this guide, you will learn how to:
- Pass HTTP headers using
headerParams - Pass HTTP headers using
customHeaderParams - Possible usage scenarios
Pass HTTP headers using headerParams
Use the headerParams capability for W3C protocol and browserstack.headerParams capability for JSON wire protocol in your test scripts to pass context. This capability accepts a JSON string with up to 5 key-value pairs as HTTP headers.
MutableCapabilities capabilities = new MutableCapabilities();
HashMap<String, Object> browserstackOptions = new HashMap<String, Object>();
browserstackOptions.put("headerParams", "{\"header_param_key1\":\"header_param_value1\", \"header_param_key2\":\"header_param_value2\"}");
capabilities.setCapability("bstack:options", browserstackOptions);
Length of each key or value in headerParams or browserstack.headerParams must be less than 500 characters.
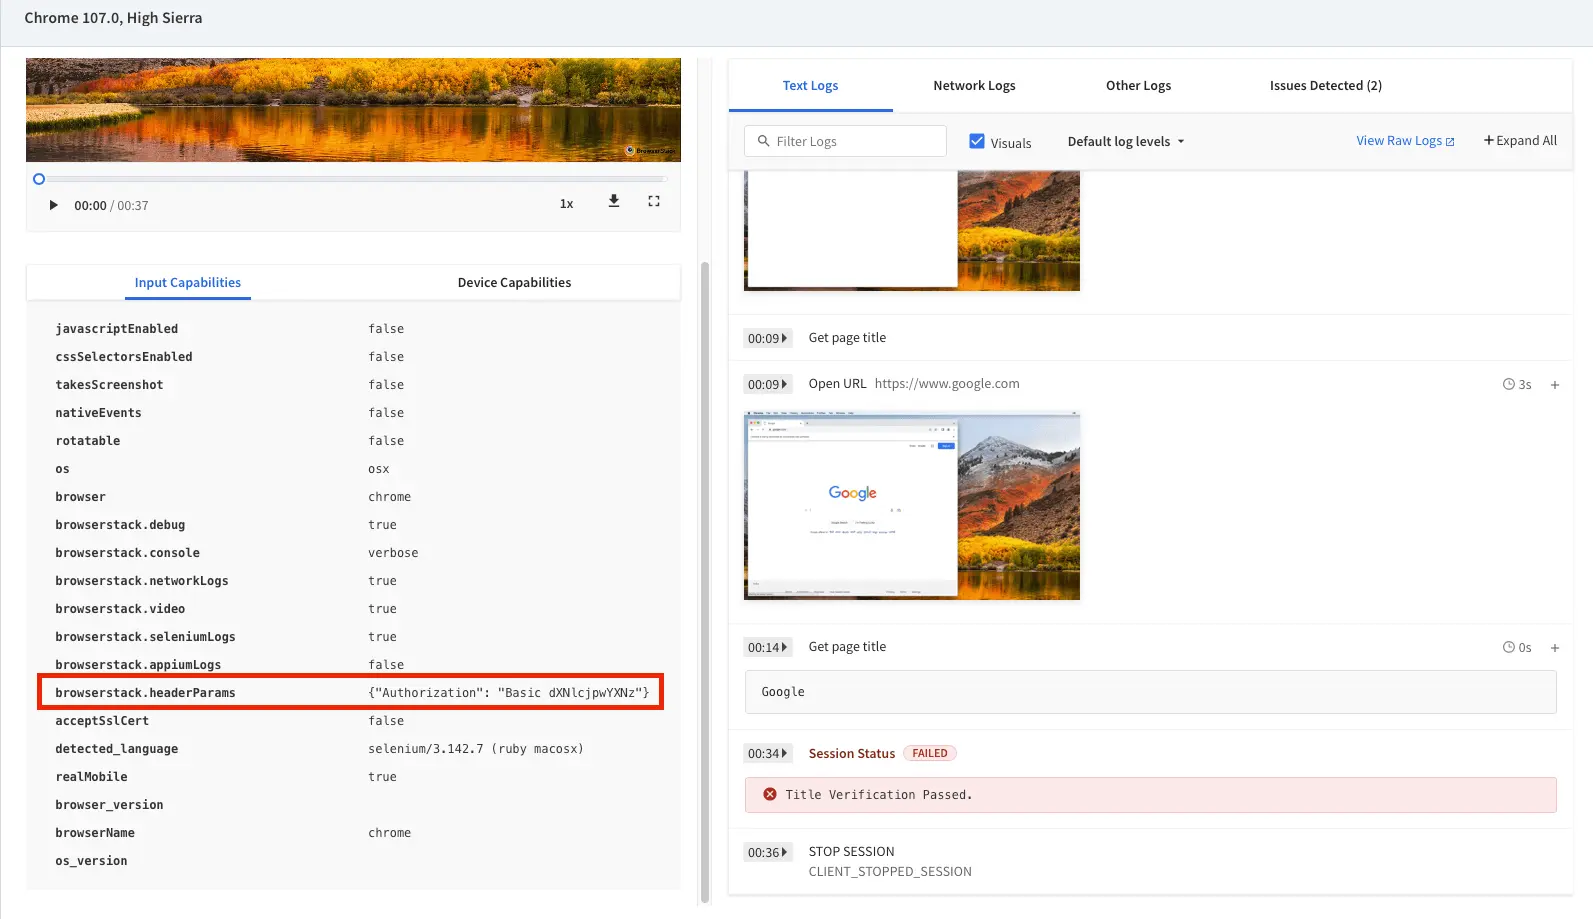
The following image shows an HTTP header, Authorization, passed as part of the HTTP request in a test session.
Pass HTTP headers using customHeaderParams
Use the customHeaderParams capability for W3C protocol and browserstack.customHeaderParams capability for JSON wire protocol in your test scripts to pass headers that apply to specific domains. This capability accepts a JSON string containing an array of rules, where each rule specifies headers and optional domain-matching criteria.
customHeaderParams is supported only for Windows and macOS devices running Chrome, Edge, Firefox, and Safari browsers. The capability is available for Selenium and Appium sessions only. To enable header injection, set the networkLogs capability to true, as shown in the following code samples.
MutableCapabilities capabilities = new MutableCapabilities();
HashMap<String, Object> browserstackOptions = new HashMap<String, Object>();
browserstackOptions.put("networkLogs", true);
browserstackOptions.put("customHeaderParams", "[{\"headers\": {\"X-Auth\": \"abc\"}, \"includeDomains\": [\"example.com\"]}, {\"headers\": {\"X-Trace\": \"1\"}, \"excludeDomains\": [\"cdn.example.com\"]}, {\"headers\": {\"X-Global\": \"1\"}}]");
capabilities.setCapability("bstack:options", browserstackOptions);
Limits and constraints:
- Maximum of 5 header key-value pairs across all rules.
- Each header key and value must be less than 500 characters.
- You cannot specify
customHeaderParamsandheaderParamsin the same session. If you declare both, the session fails to start. -
customHeaderParamsrules are silently dropped on real mobile devices (Android and iOS). UseheaderParamsfor mobile device support.
Domain-matching semantics
When you specify domain rules for customHeaderParams, BrowserStack matches each rule against the request hostname, lowercased and with the port removed:
-
Plain string: matches the exact domain and its subdomains. For example,
example.commatchesexample.com,www.example.com, anda.b.example.com. -
Regex pattern: matches domains against a regex written as
/pattern/flags. Only thei(case-insensitive) andm(multiline) flags are supported. All other flags are ignored. -
No
includeDomains: if a rule omitsincludeDomains, its headers apply to all domains. -
excludeDomainsprecedence: when a rule specifies bothincludeDomainsandexcludeDomains,excludeDomainstakes precedence.
Possible usage scenarios
You can use Default HTTP headers with custom headers for situations like:
- Support for third-party integration that requires passing authentication details to allow access to restricted sites.
- Pass additional context to identify different requests when using mocking servers.
- Pass custom headers, such as your BrowserStack Access Key, to applications, such as AWS Web Application Firewall to identify where a request originates from.
We're sorry to hear that. Please share your feedback so we can do better
Contact our Support team for immediate help while we work on improving our docs.
We're continuously improving our docs. We'd love to know what you liked
We're sorry to hear that. Please share your feedback so we can do better
Contact our Support team for immediate help while we work on improving our docs.
We're continuously improving our docs. We'd love to know what you liked
Thank you for your valuable feedback!